Protect sensitive and classified data before the OS ever loads. Cigent enforces authentication at power on and secures Data at Rest (DAR), protecting mission data on endpoints, servers, and deployed systems using Cigent secure SSDs, Pre-Boot Authentication (PBA), and Software Full Drive Encryption (FDE).
Connect with an Expert
Cigent’s full-stack Data at Rest solution is built for U.S. defense programs operating under strict data protection requirements, including the NSA CSfC Data at Rest Capability Package, where physical access to a device is part of the threat model, not a remote edge case.
Threat assumptions often include:
The Cigent Difference
Cigent enforces authentication at power-on and keeps data encrypted until access is verified. If authentication fails, the system does not boot, reducing exposure to offline access and pre-OS bypass attempts.
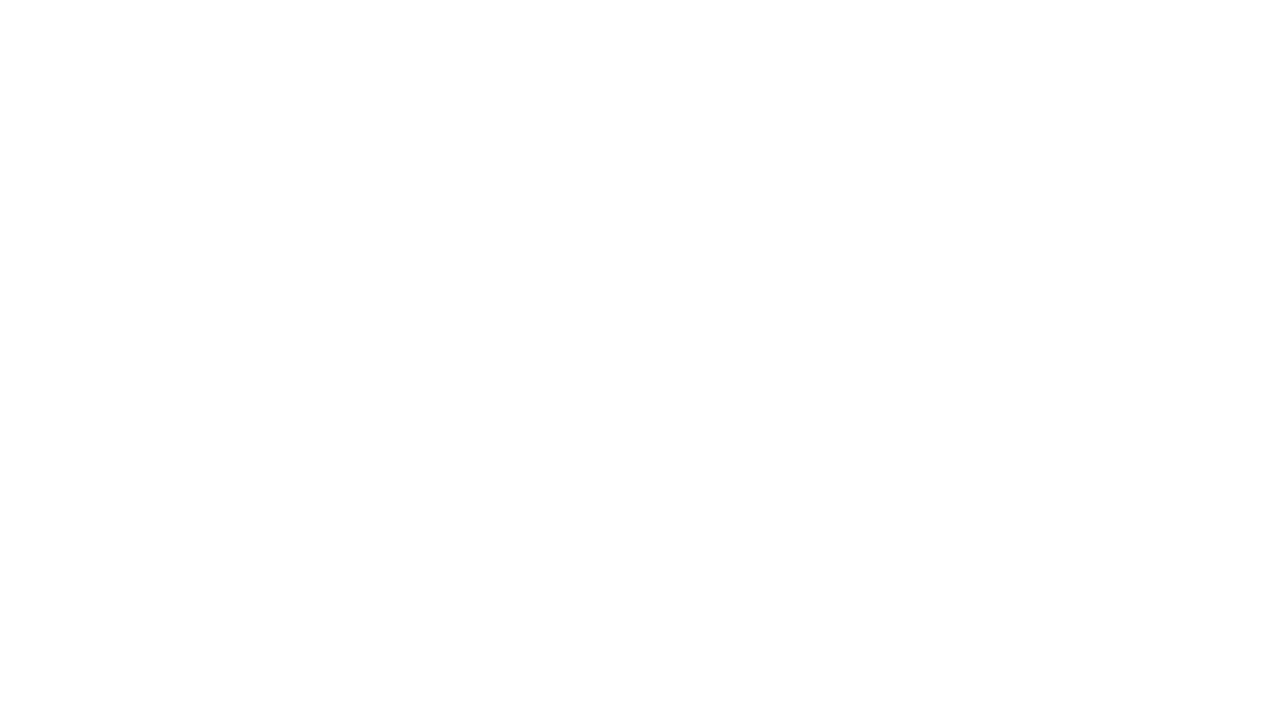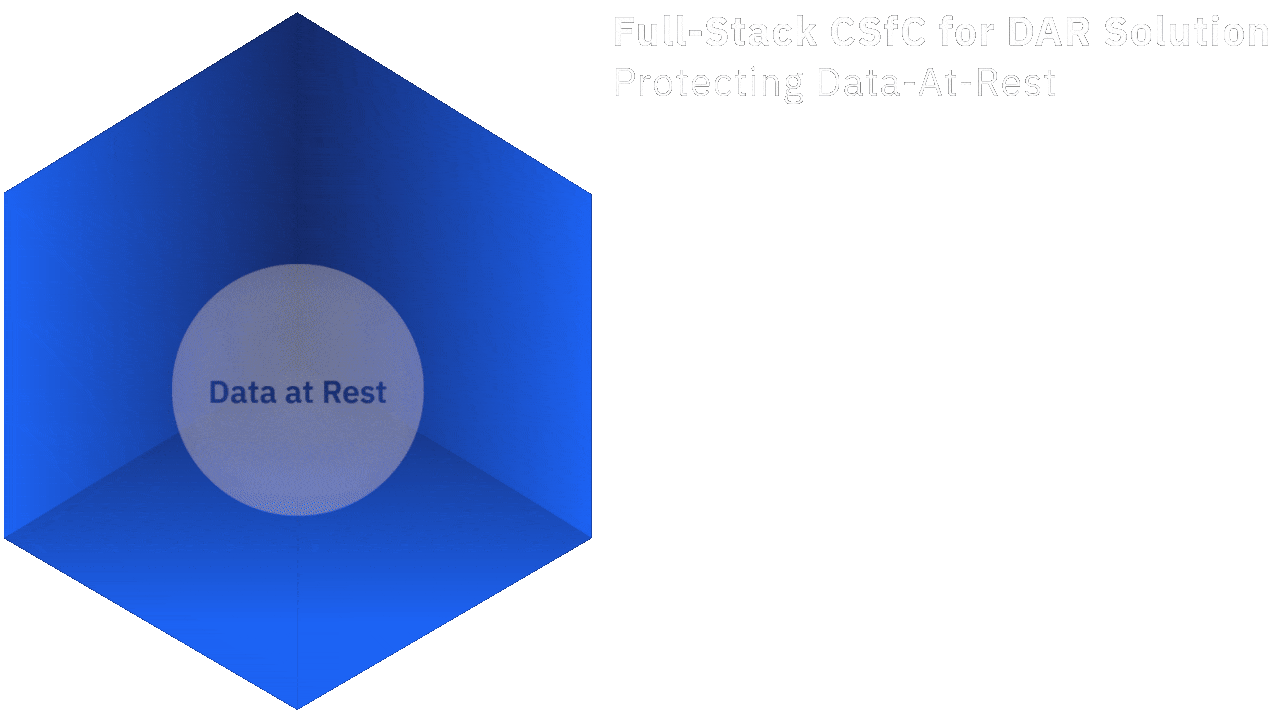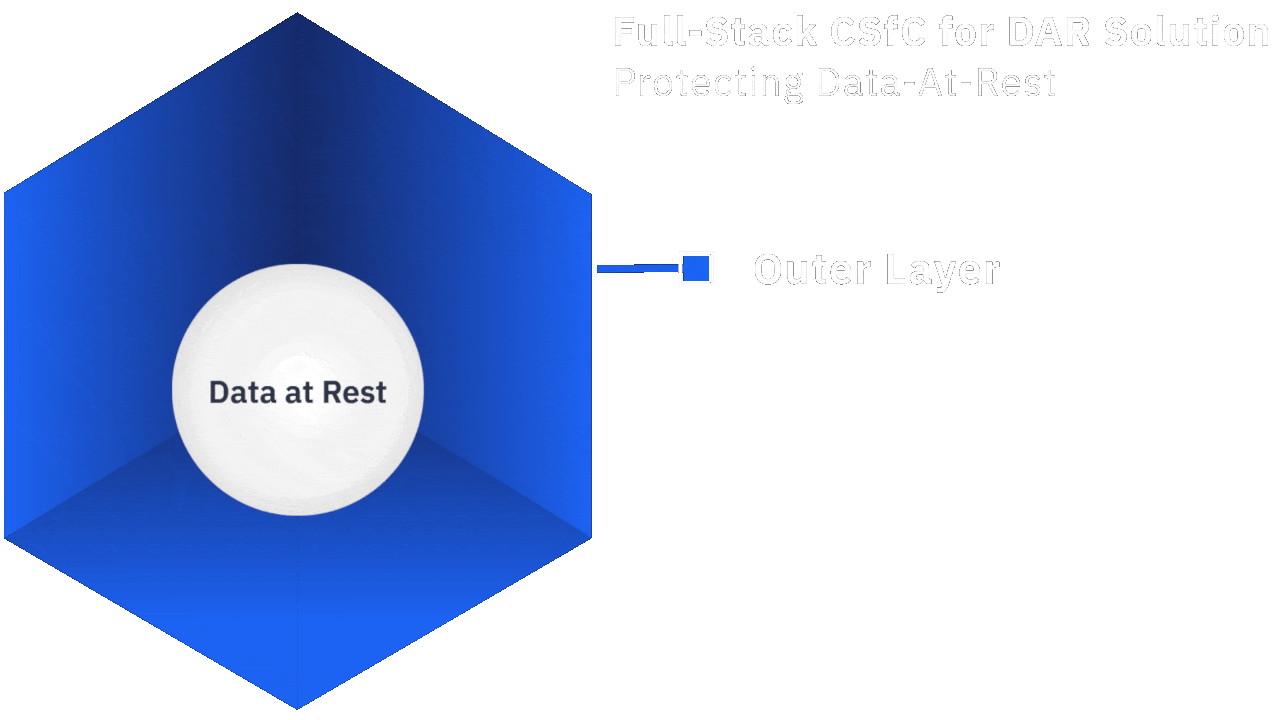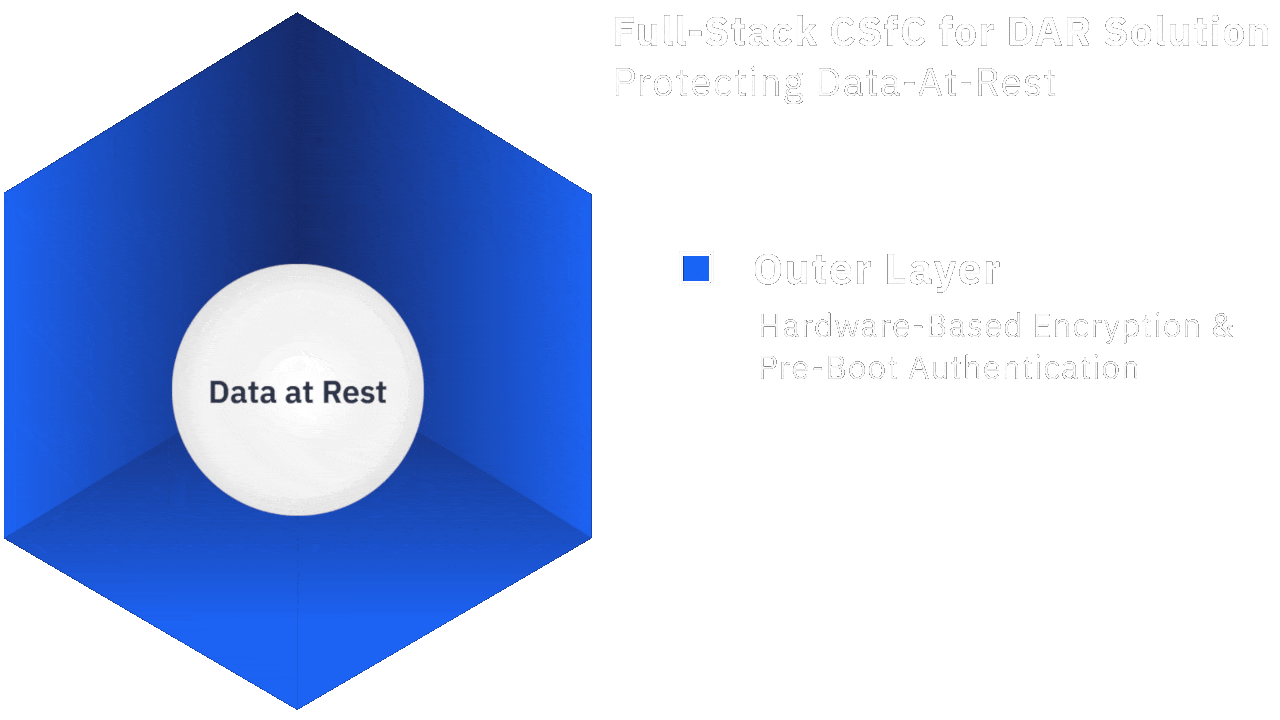
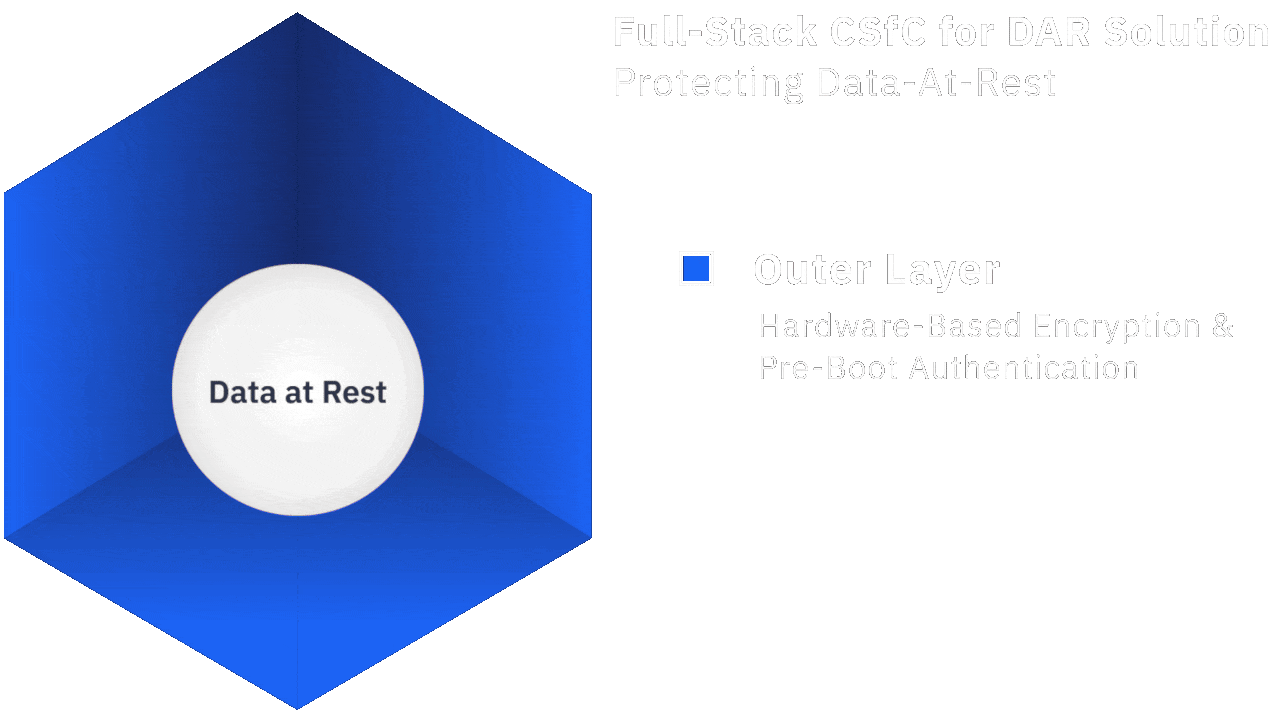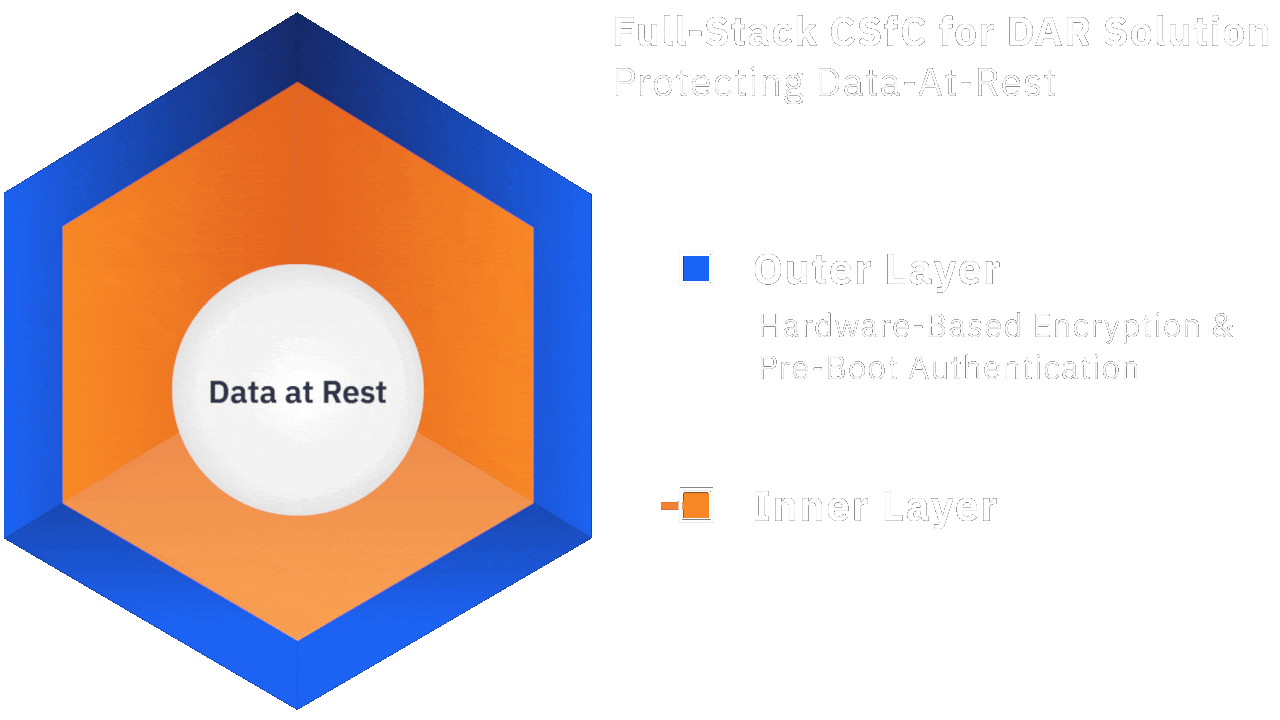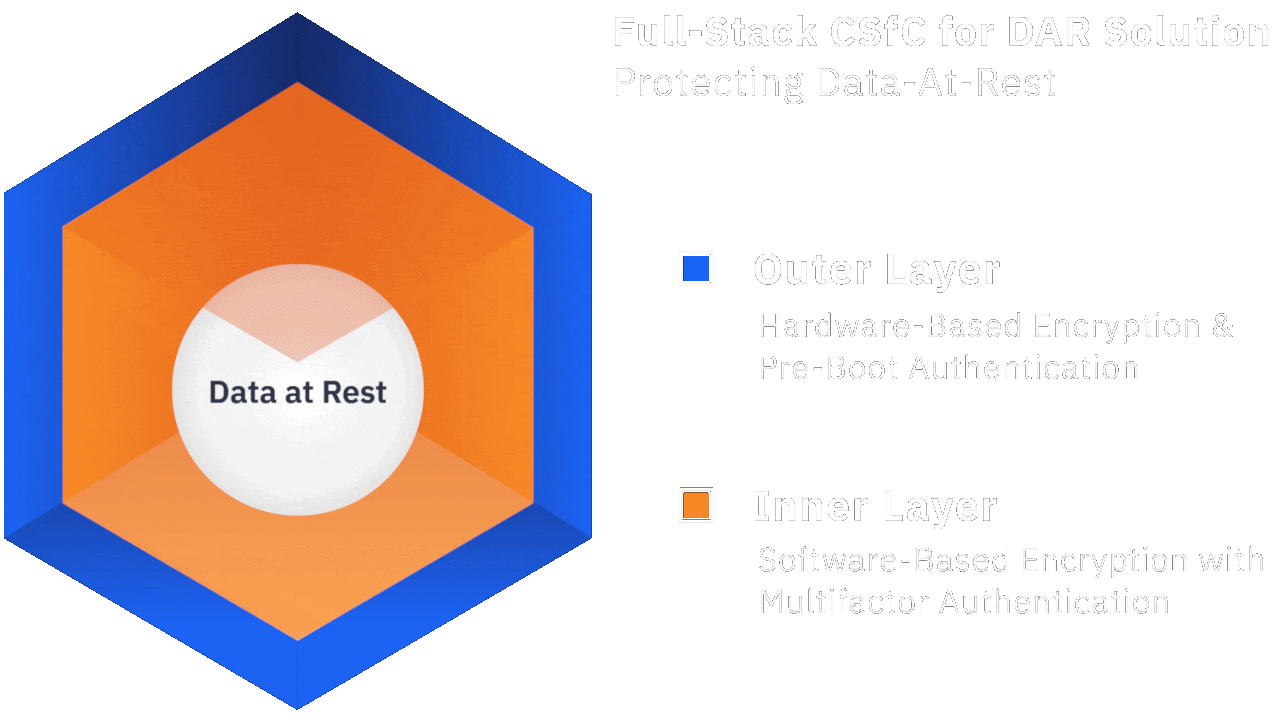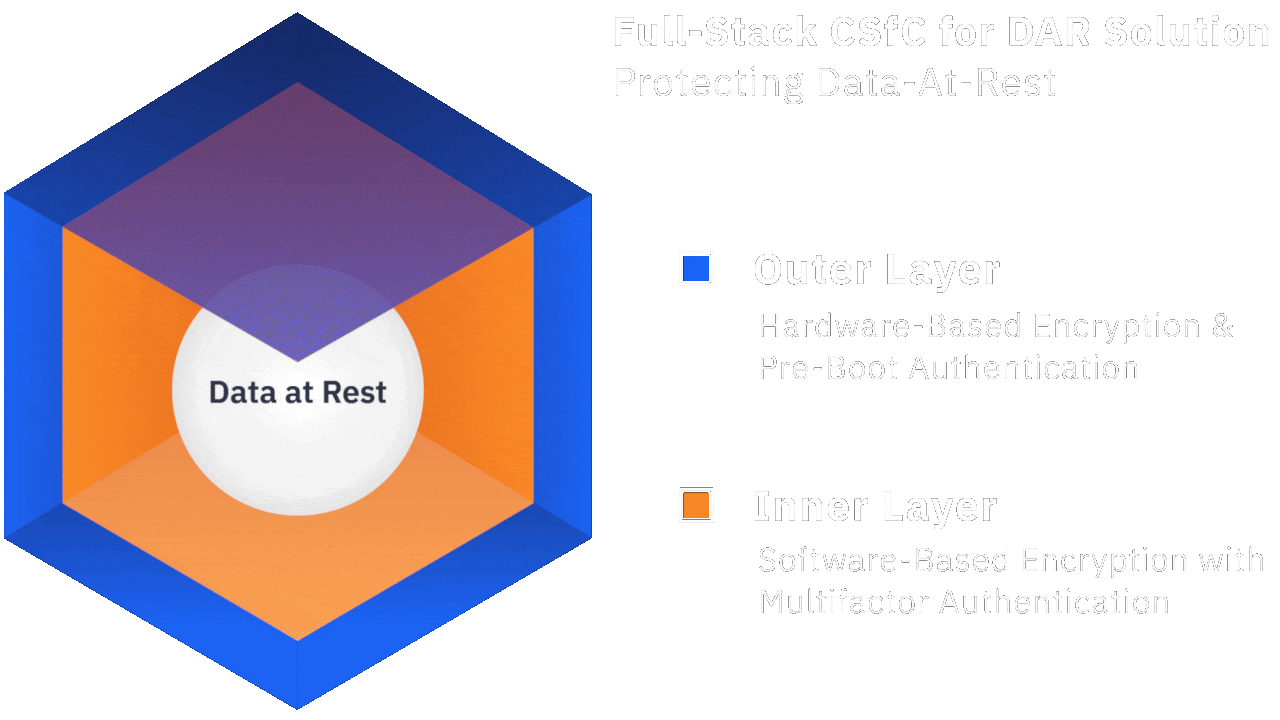
Hardware Full Drive Encryption (HW FDE) combined with PBA. This is the outer layer of the dual-layer encryption approach mandated by the Commercial Solutions for Classified (CSfC) Data-at-Rest (DAR) program and provides the first layer of defense. It includes:
Software Full Drive Encryption (SW FDE) with Multi-Factor Authentication (MFA). This is the inner layer of the dual-layer encryption approach mandated by the Commercial Solutions for Classified (CSfC) Data-at-Rest (DAR) program. It provides independent protection after the outer layer has been unlocked. It includes:
When loss of a single device triggers contractual or reporting consequences, encryption must be enforced at the earliest operational stage.
Outcomes
This is endpoint level Zero Trust applied at system start.
Secure sensitive Data at Rest with Software Full Drive Encryption and Pre-Boot Authentication.
Schedule a ConsultationLearn how to secure mission-critical and classified data across the battlespace.