Safeguard Classified Mission Data

Protect sensitive and classified data before the OS ever loads. Cigent enforces authentication at power on and secures Data at Rest (DAR), protecting mission data on endpoints, servers, and deployed systems using Cigent secure SSDs, Pre-Boot Authentication (PBA), and Software Full Drive Encryption (FDE).

Connect with an Expert
How Cigent Helps

Built for Devices Operating at the Edge

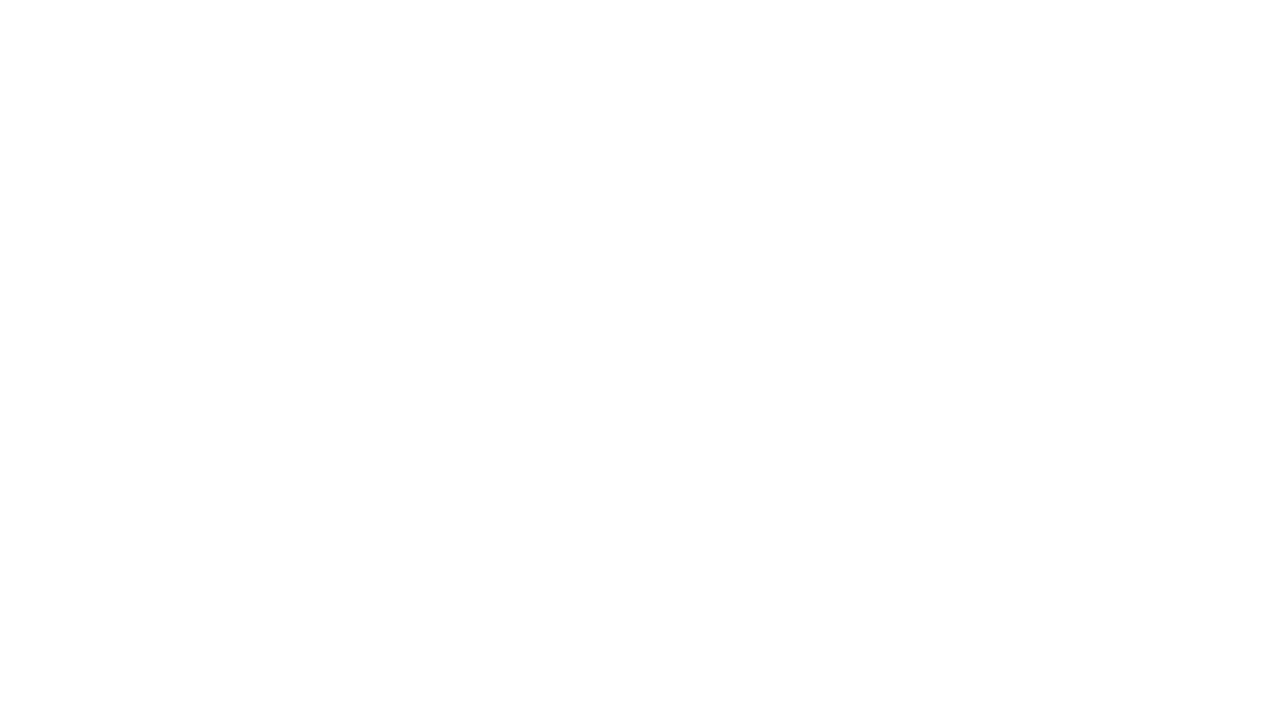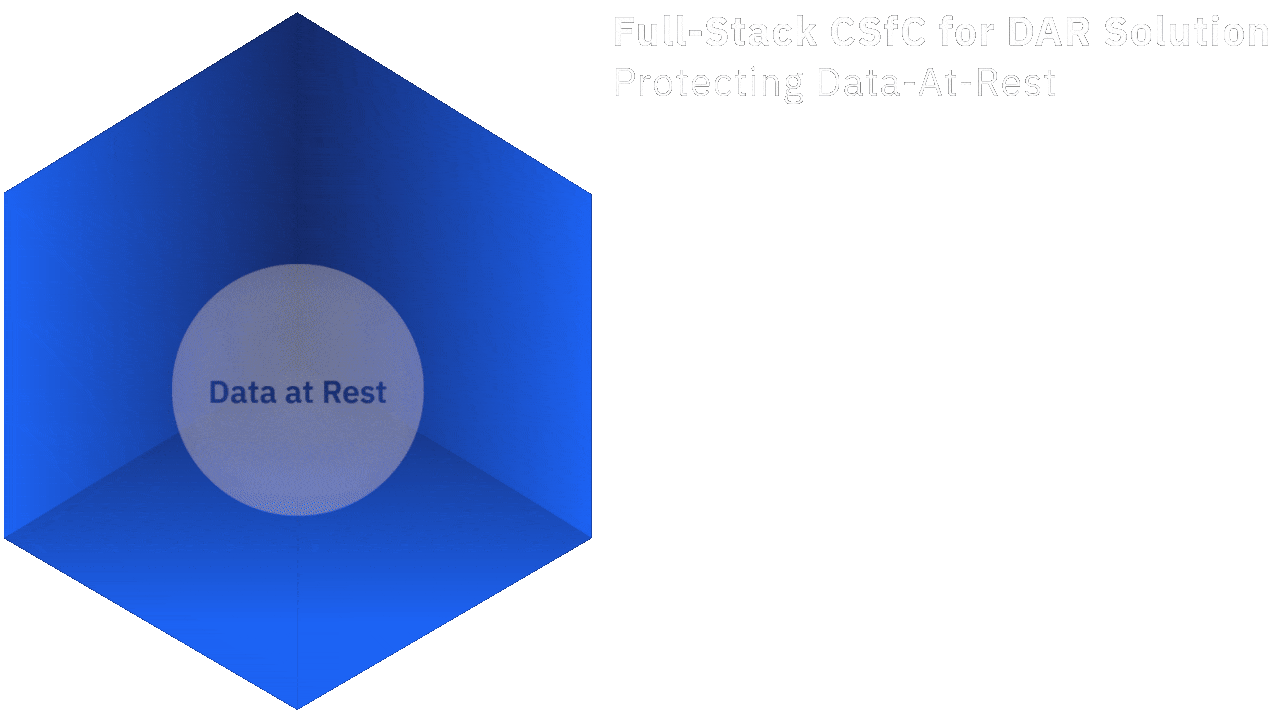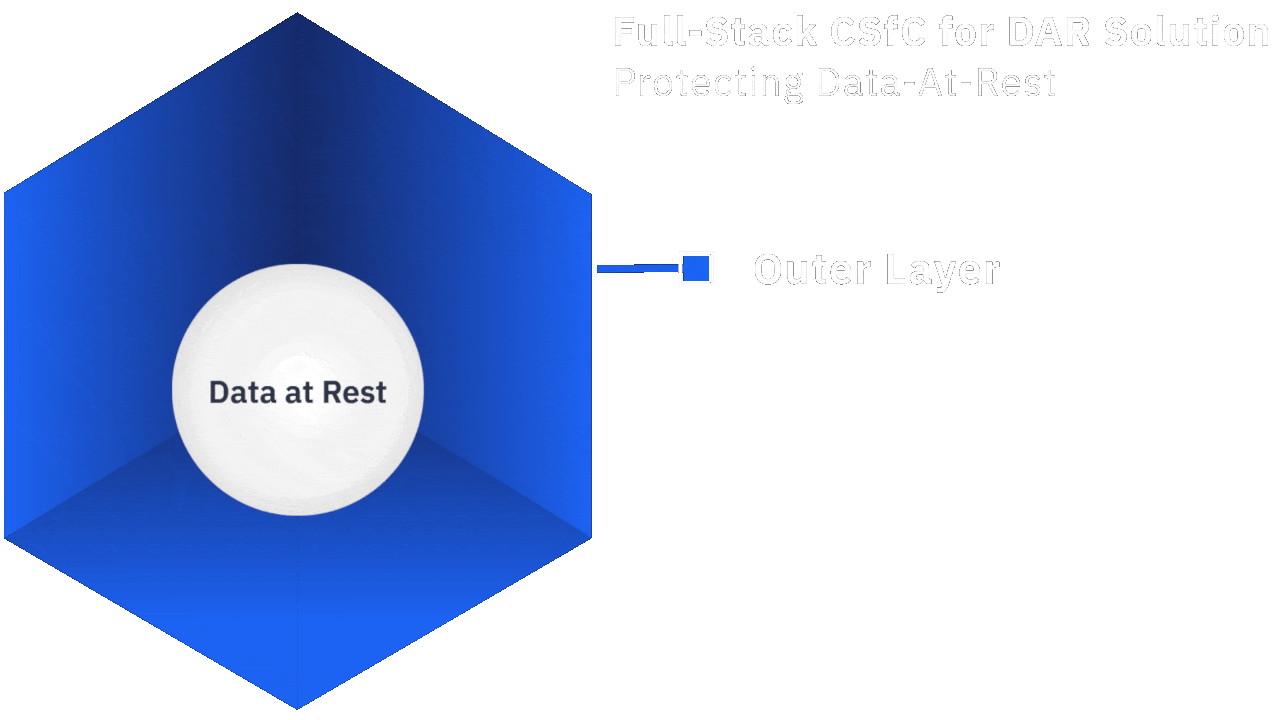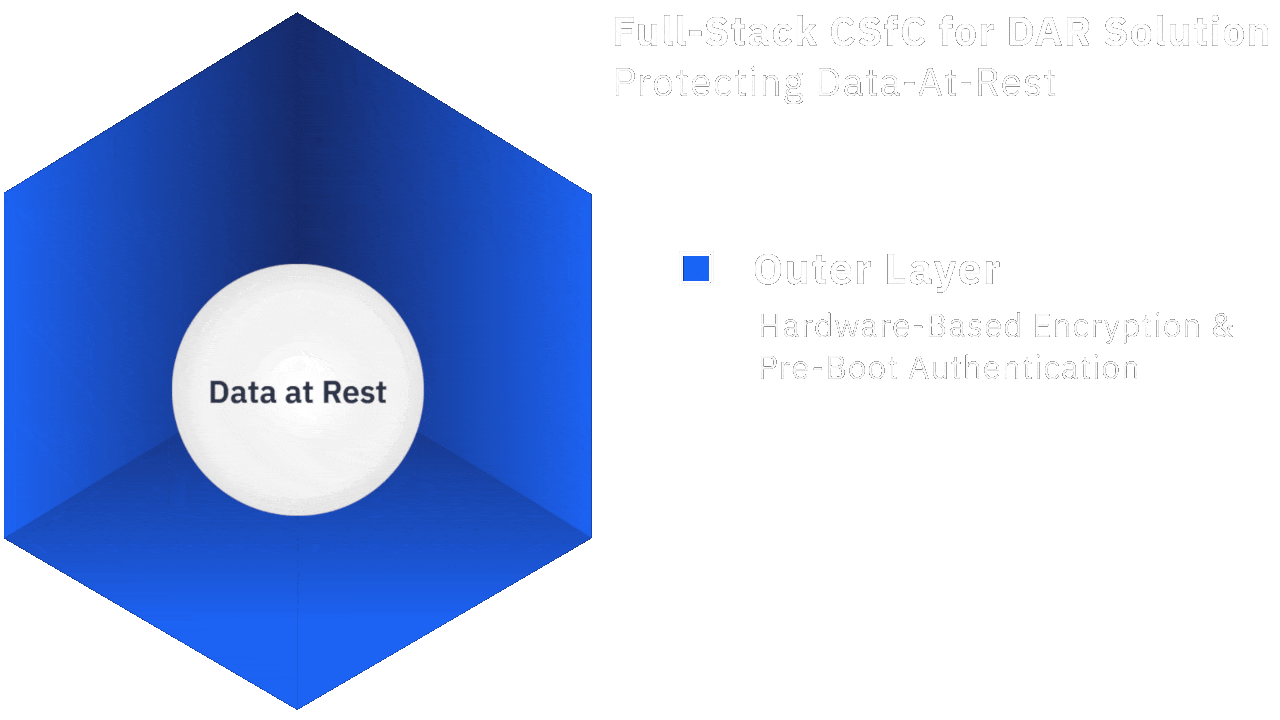
Cigent’s full-stack Data at Rest solution is built for U.S. defense programs operating under strict data protection requirements, including the NSA CSfC Data at Rest Capability Package, where physical access to a device is part of the threat model, not a remote edge case.

Threat assumptions often include:

  • Physical device loss or confiscation
  • Exposure during field operations
  • Credential compromise attempts
  • Offline access to the drive

The Cigent Difference

Cigent enforces authentication at power-on and keeps data encrypted until access is verified. If authentication fails, the system does not boot, reducing exposure to offline access and pre-OS bypass attempts.
Used & Trusted by Top Federal and Defense Agencies

Advanced Data Protection

Dual-Layered Encrypytion Approach

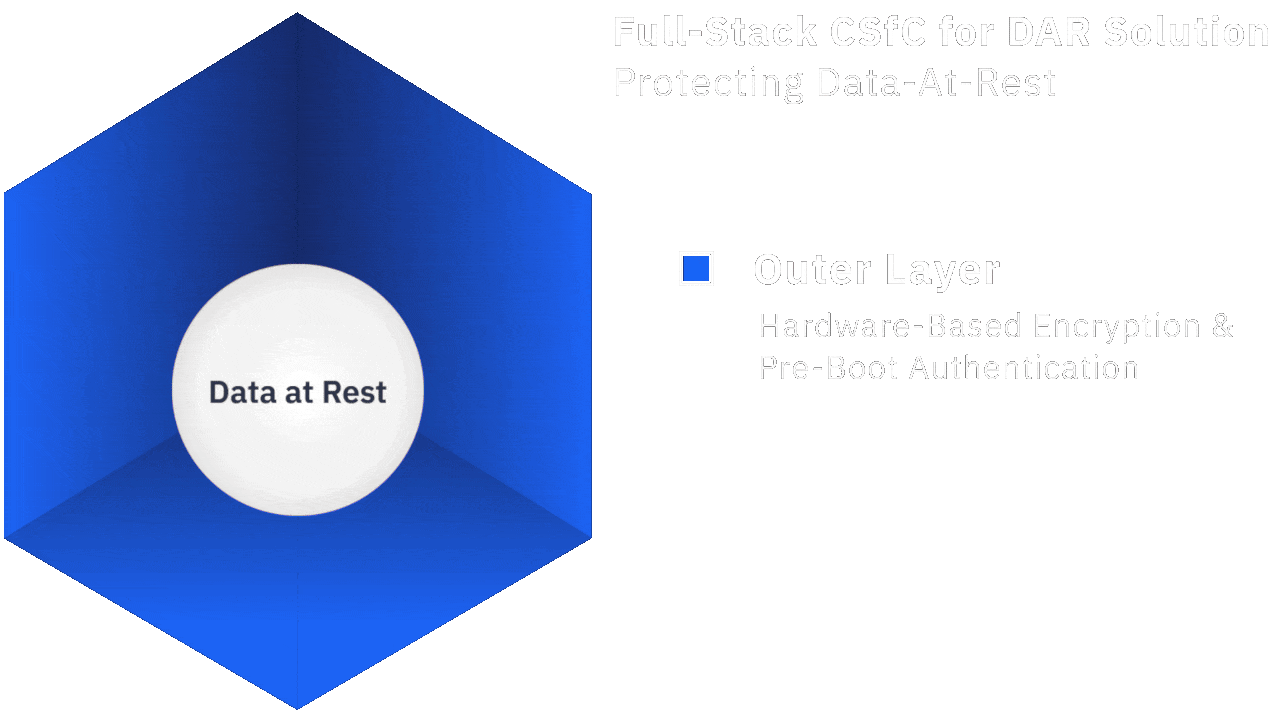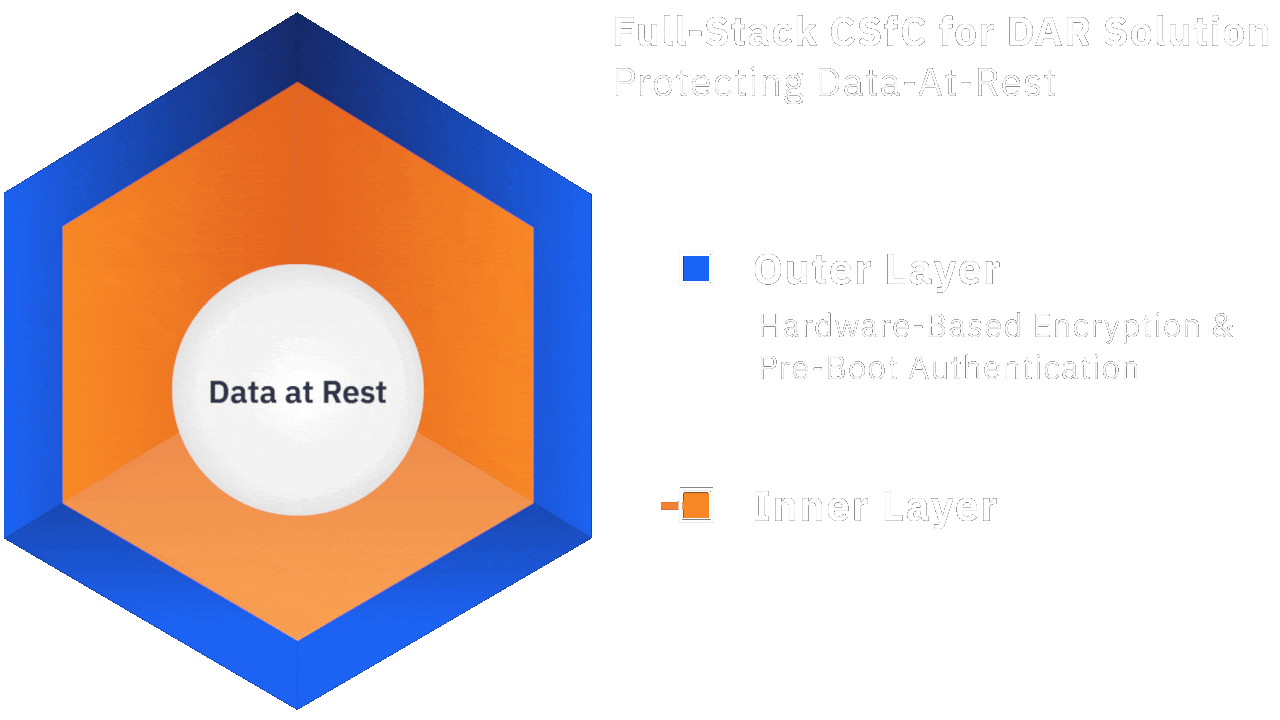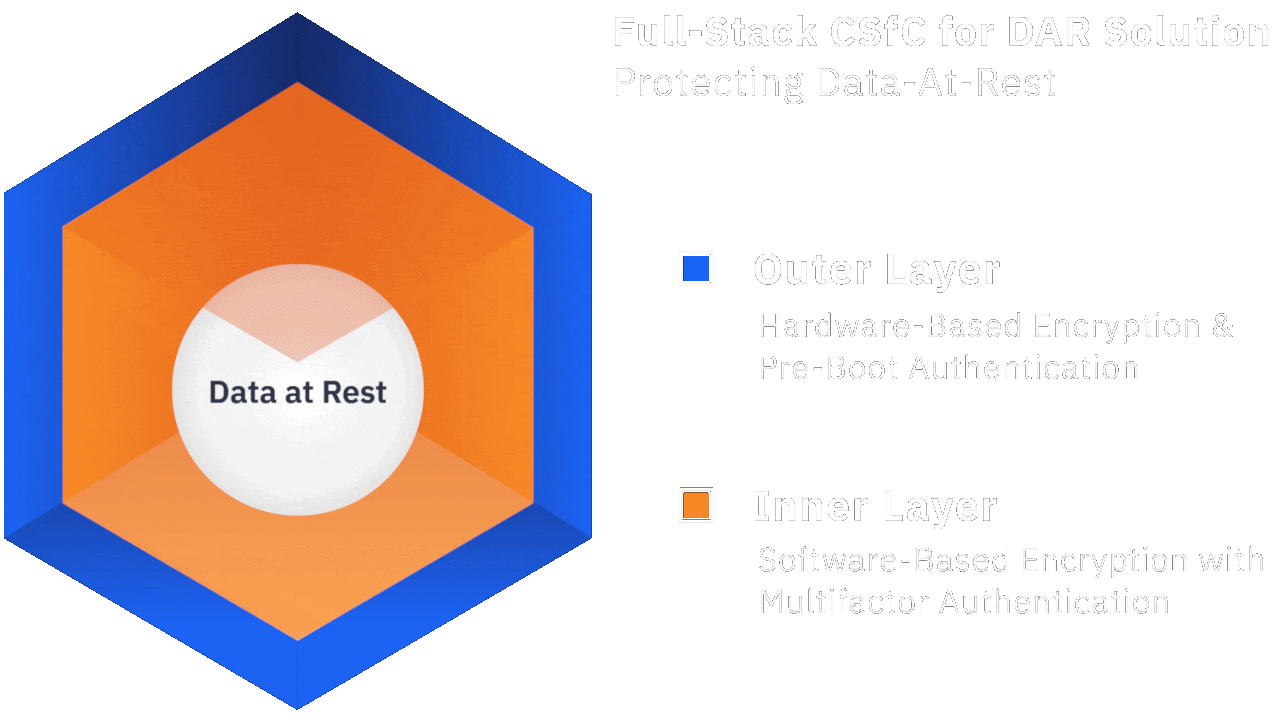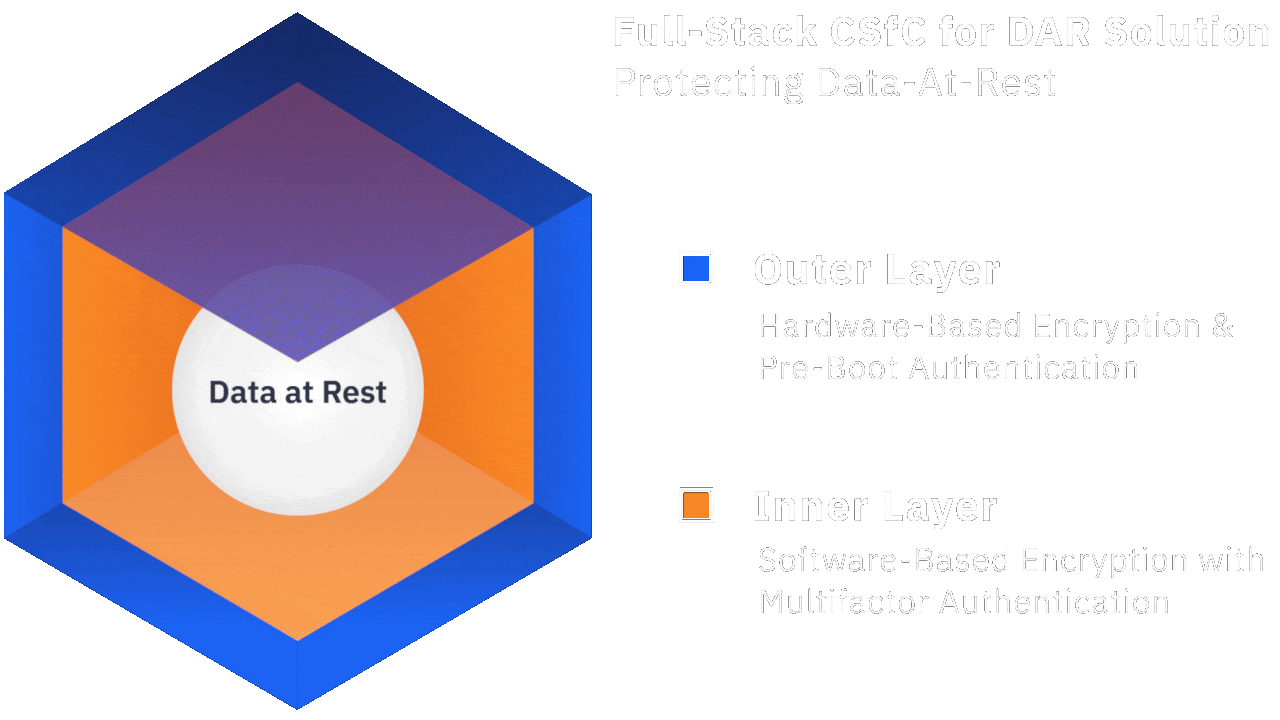
Hardware Full Drive Encryption (HW FDE) combined with PBA. This is the outer layer of the dual-layer encryption approach mandated by the Commercial Solutions for Classified (CSfC) Data-at-Rest (DAR) program and provides the first layer of defense. It includes:

  • AES-256 Hardware Encryption
    • Provides robust encryption, safeguarding keys from interception.
  • Pre-Boot Authentication (PBA)
    • Secure login before the operating system loads, defending against boot-level threats.

Designed For Regulated and Mission Critical Data Environments

  • Defense contractors handling controlled data
  • Federal endpoint fleets
  • Distributed and mobile mission teams
  • Regulated and compliance driven deployments

When loss of a single device triggers contractual or reporting consequences, encryption must be enforced at the earliest operational stage.

Outcomes

  • Reduced exposure from lost or stolen endpoints
  • Enforced access control at power on
  • Protection against offline attacks
  • Strengthened compliance alignment
  • Consistent encryption policy enforcement

This is endpoint level Zero Trust applied at system start.

Testimonials

"Cigent meets a critical need in defense and intelligence by protecting our vulnerable data on endpoint devices. Their layered approach prevents unauthorized access—even against the advanced threats we face. Because of their operational heritage, deep data protection expertise, and strong mission focus, they’re a trusted partner in securing our government's sensitive information."

Teresa Shea
Former Director Signals Intelligence NSA

Enforce Access Before Boot

Secure sensitive Data at Rest with Software Full Drive Encryption and Pre-Boot Authentication.

Schedule a Consultation

Frequently Asked Questions

Still have Questions?

Learn how to secure mission-critical and classified data across the battlespace.