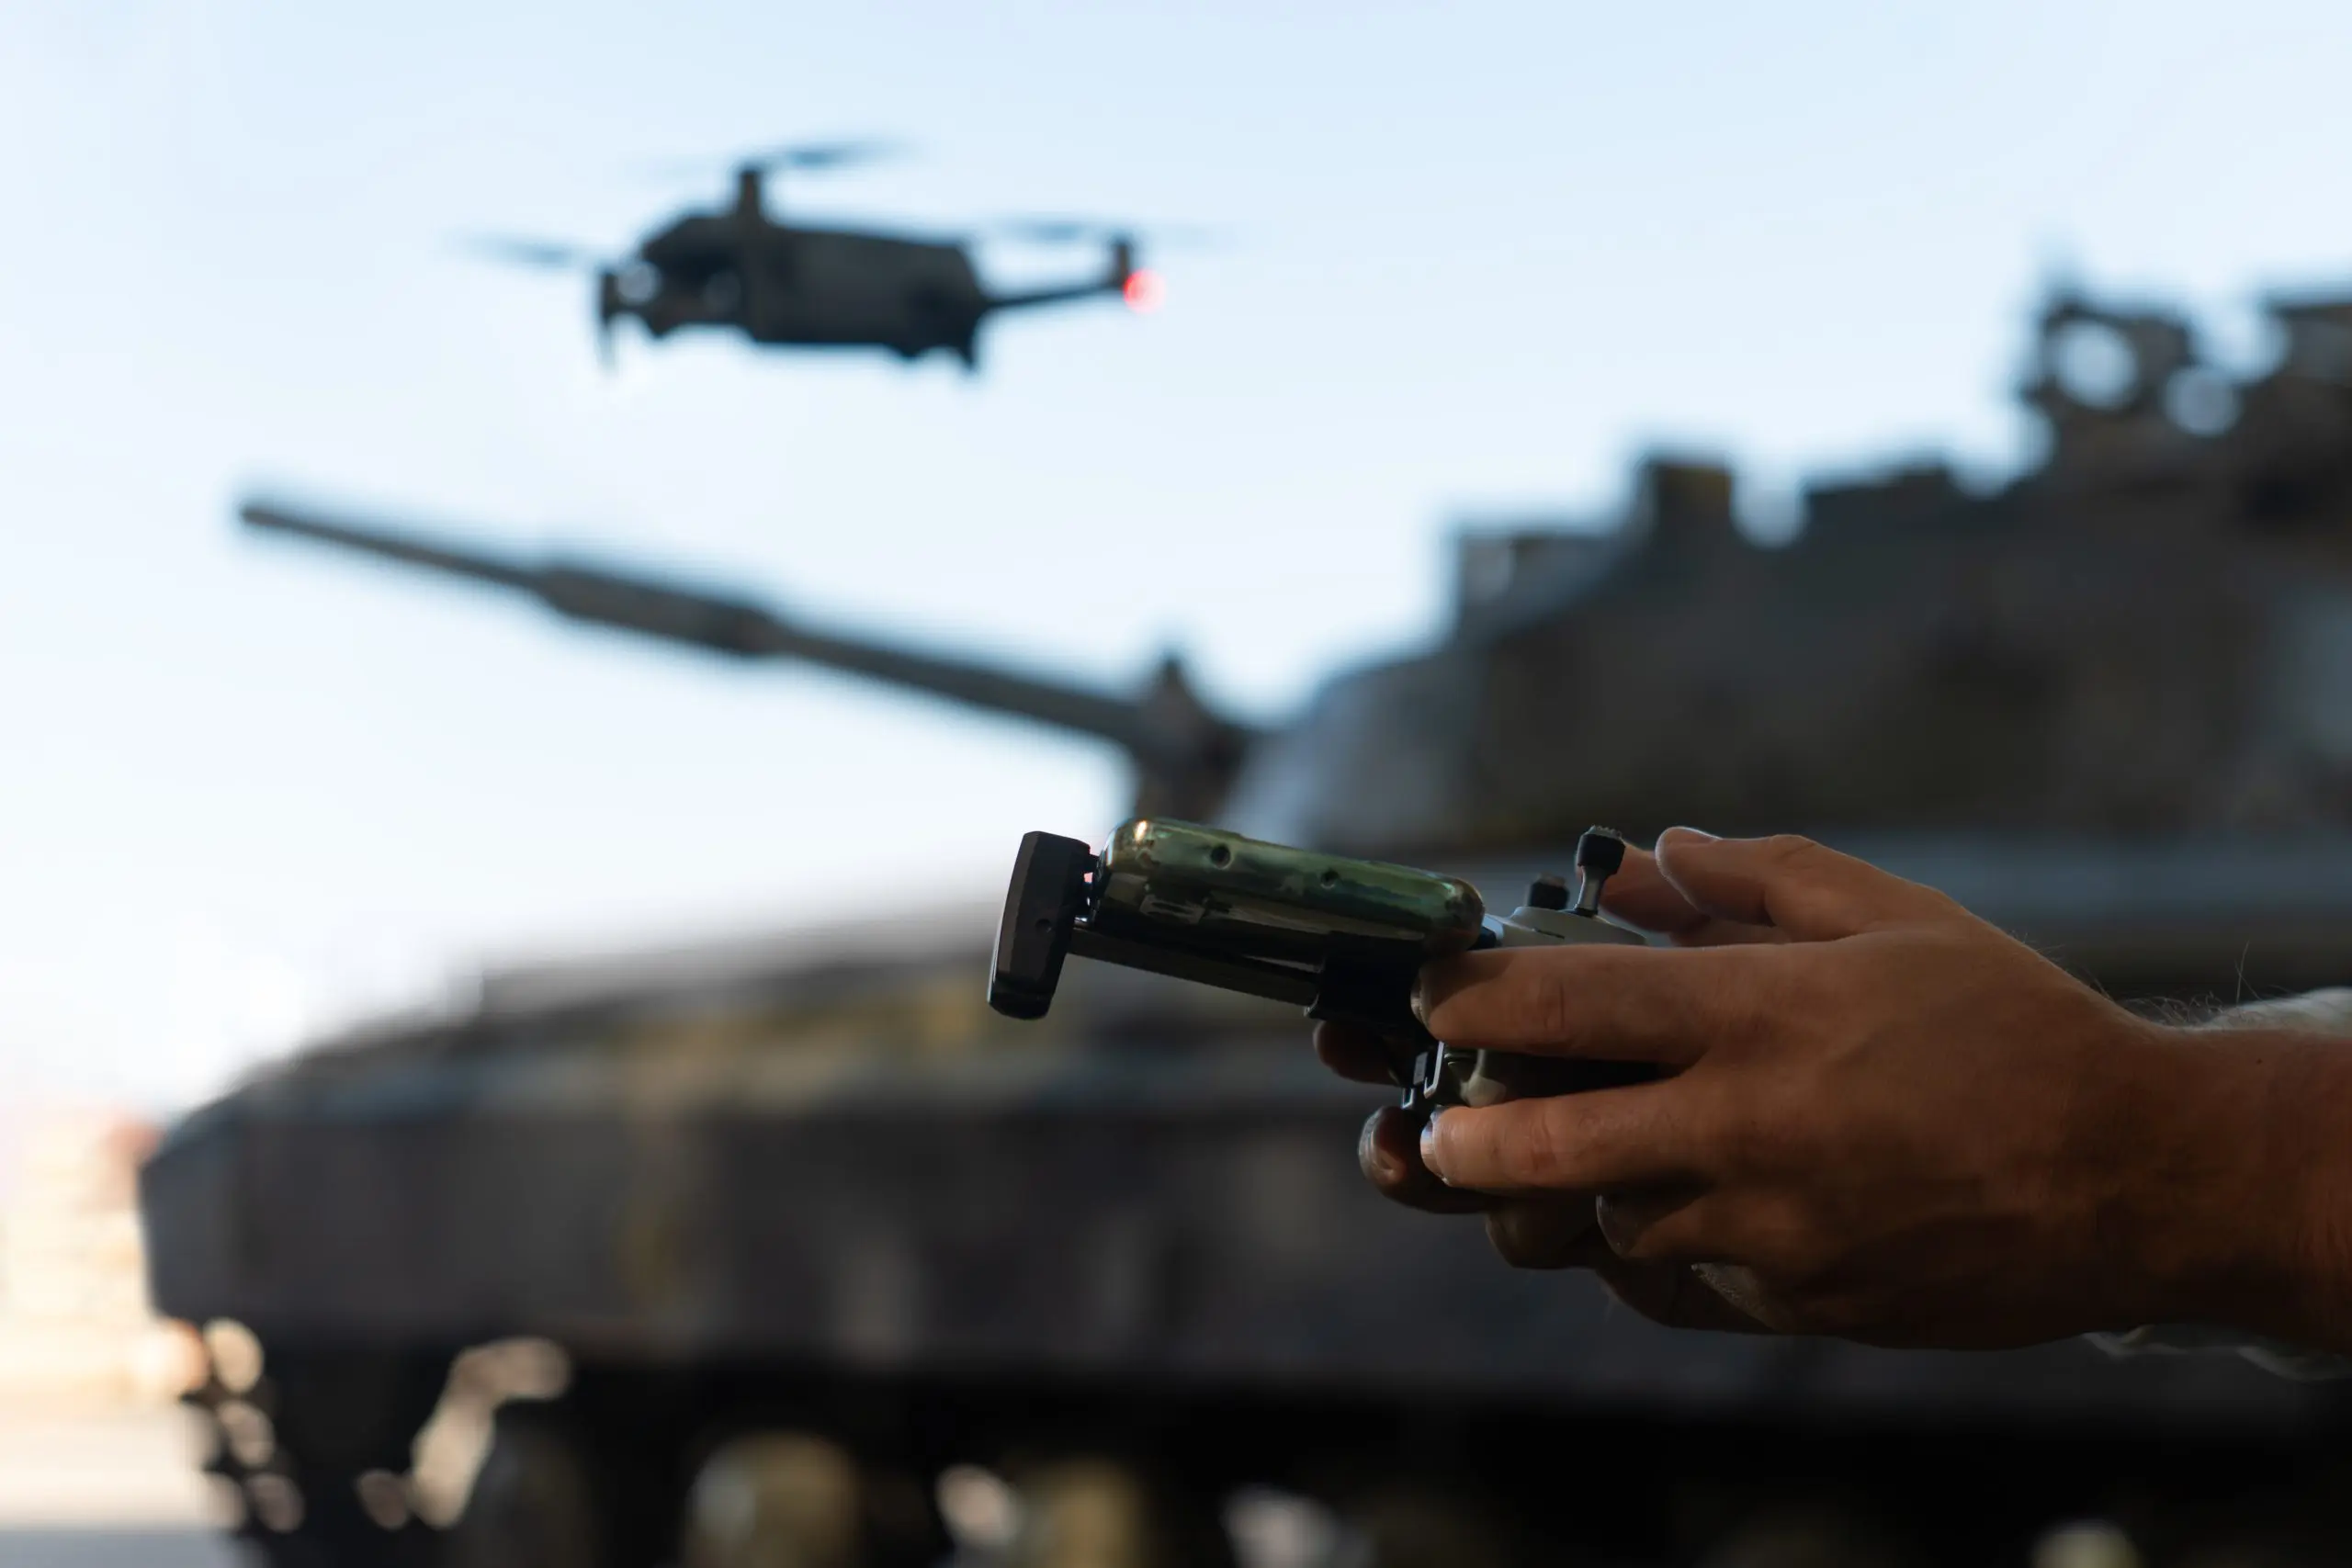
The mission was routine until it wasn’t. A small unmanned aerial vehicle was conducting reconnaissance over contested terrain, collecting high-resolution imagery and logging environmental data. Mid-flight, communication dropped. Whether due to jamming, mechanical failure, or hostile interception, the outcome was the same: the platform was gone, and this is not a hypothetical scenario as seen in incidents like the capture of a U.S. RQ-170 Sentinel drone by Iran.
But the real question came next. What happened to the data?
Key Takeaways
- Losing the platform must not mean losing the mission: Unmanned systems store mission logs, sensor payloads, targeting data, and comms records; capture of the airframe is recoverable, capture of readable data is not.
- Adversary recovery is documented, not hypothetical: Captured platforms have had storage removed and analyzed; assume the device will be in hostile hands and design for that moment.
- Encryption must not depend on the platform being alive: Protection has to hold with the system powered off, crashed, or disassembled, which means hardware encryption gated by authentication, not OS-level controls.
- Two independent layers is the classified standard: The NSA CSfC DAR architecture, hardware encryption with pre-boot authentication plus independent software FDE, is built for exactly this loss scenario.
- Emergency sanitization closes the loop: Verified erasure, executable locally or remotely, means a downed platform can carry nothing worth recovering.
The Stakes Behind a Lost Platform
Unmanned systems rarely operate empty. Inside their storage systems lives the real mission payload:
- Mission logs detailing routes, timestamps, and operational decisions
- Sensor data and high-value imagery
- Embedded algorithms and AI models
- Encryption keys and communication configurations
This matters because adversaries have actively attempted to extract and analyze data from captured drones. If that data falls into the wrong hands, the consequences extend far beyond a single lost asset. Adversaries can reconstruct mission intent, reverse-engineer capabilities, and exploit vulnerabilities in future operations. In other words, losing the platform can mean losing the mission. Unless data at rest is properly secured.
What Data at Rest Means on an Unmanned System
On an unmanned system, data at rest includes the mission data stored locally on the platform, from mission logs and sensor captures to AI models, communications records, and telemetry. When that system is lost, disabled, or captured, this stored-data footprint can remain on the device even after the mission ends, making protection of the data itself critical.
Scenario One: Unprotected Storage
The same UxV goes down, but this time its onboard storage is unprotected. No encryption. No access controls. No secure partitioning.
An adversary recovers the device and removes the storage module, beginning analysis similar to documented cases of recovering sensitive mission data from captured systems, they begin analysis:
- File systems are mounted with ease
- Mission logs reveal operational patterns
- Imagery provides intelligence insights
- Proprietary algorithms are extracted and studied
Even if the system used encryption during transmission, it does not matter. Data at rest becomes the weakest link. This is the reality of offline attacks. When an attacker has physical possession, time and persistence are on their side.
Scenario Two: Protected by Design
Now consider the same situation with a different outcome. The platform is lost, but its storage was secured from the start using a layered Data at Rest strategy.
Pre-Boot Authentication (PBA)
Before any data can be accessed, the system requires authentication at boot. Without valid credentials, the storage remains locked. There is no operating system access, no file system visibility, and no easy entry point. An attacker attempting to bypass PBA faces hardened protections designed specifically for offline scenarios.
Full Drive Encryption
Every bit of data on the drive is encrypted. Even if the storage is removed and connected to another system, it appears as unreadable ciphertext. This is critical in physical capture scenarios. Encryption ensures that possession of the hardware does not equal access to the data.
Secure Partitions
Not all data carries the same level of sensitivity. Secure partitioning isolates mission-critical data from less sensitive components. This segmentation reduces risk and limits exposure. Even in the unlikely event of partial compromise, the most sensitive assets remain protected.
Crypto Erase and Block Erasure
When a platform is at risk of capture, time is everything. Crypto erase enables rapid destruction of encryption keys, rendering all encrypted data instantly inaccessible. Without the keys, the data becomes useless. Block erasure adds another layer, targeting specific data regions for destruction when needed. These capabilities ensure that even in worst-case scenarios, data cannot be exploited.
Verified Sanitization
After a loss event, confidence matters. Verified sanitization provides assurance that data has been fully and irreversibly destroyed. This is not a best-effort deletion. It is a provable outcome that meets strict security requirements. For mission planners and operators, this closes the loop. The platform may be gone, but the data is not recoverable.
Why Data at Rest Security is Different for UxV
Unmanned systems operate in environments where physical security cannot be guaranteed, with ongoing losses of high-value drones in contested environments reinforcing this risk. Unlike traditional endpoints, they are:
- Deployed in hostile or remote locations
- Vulnerable to capture and reverse engineering
- Often disconnected from networks during operation
This makes Data at Rest protection essential, not optional.
DAR strategies must assume:
- The attacker has full physical access
- The attacker can perform offline analysis
- The attacker has unlimited time and resources
Anything less leaves a critical gap.
Mission Assurance Starts Before Deployment
The difference between the two scenarios is not luck. It is preparation. By integrating pre-boot access control, full drive encryption, secure partitioning, crypto and block erasure, and verified sanitization organizations can ensure that the loss of a platform does not translate into a loss of mission data.
The Bottom Line
In modern operations, data is often more valuable than the platform itself. Unmanned systems will be lost. That is an operational reality. The question is whether those losses create intelligence opportunities for adversaries or dead ends. With the right Data at Rest protections in place, the answer is clear.
You can lose the platform without losing the mission. Get a consultation and see if your organization is protected.
Frequently Asked Questions
What is data at rest on unmanned systems?
Data at rest is mission data stored locally on an unmanned system rather than data actively moving across a network. On UxVs, this can include mission logs, sensor data, imagery, embedded algorithms, AI models, encryption keys, and communication configurations that remain on onboard storage during and after a mission.
What data do UxVs store?
UxVs can store mission logs containing routes, timestamps, and operational decisions, along with sensor data, high-value imagery, embedded algorithms, AI models, encryption keys, and communication configurations. If the platform is lost or captured, this stored information can provide insight into mission activity and system capabilities.
What happens when a drone is captured?
When a drone or other unmanned platform is captured, an adversary may gain physical access to its onboard storage. Without adequate data-at-rest protection, storage can be removed and analyzed offline, potentially exposing file systems, mission logs, imagery, operational patterns, and embedded algorithms even if communications were encrypted during the mission.
Does encryption protect a captured drive?
Full drive encryption can protect data when a storage device is physically captured, provided access to the encrypted data is properly controlled. If an encrypted drive is removed and connected to another system while remaining locked, its contents appear as unreadable ciphertext rather than accessible mission data.
What is pre-boot authentication on embedded platforms?
Pre-Boot Authentication (PBA) requires authentication before the operating system loads and before protected storage becomes accessible. On embedded and unmanned platforms, this helps protect against offline access after physical capture by keeping the drive locked without valid credentials, preventing normal operating system and file system access.
What does CSfC DAR require for vehicles?
For classified data at rest, NSA’s Commercial Solutions for Classified Data at Rest architecture uses independent layers of protection. This includes hardware-encrypted storage with Pre-Boot Authentication combined with an independent software full drive encryption layer, helping protect classified mission data if a vehicle, unmanned system, or its storage is physically recovered.
Can data be erased remotely or in an emergency?
Crypto erase and block erasure can provide options for destroying protected data when a platform is at risk of capture. Crypto erase destroys the encryption keys that make encrypted data accessible, while block erasure targets stored data for destruction. Verified sanitization provides assurance that the required data was irreversibly erased.
What storage form factors fit unmanned platforms?
Storage requirements vary considerably across unmanned platforms based on size, available space, performance requirements, environmental conditions, and system architecture. Secure storage can be integrated into embedded and vehicle systems, but the appropriate drive and form factor should be selected according to the specific unmanned platform and mission requirements.
Do these protections work when the platform is disconnected?
Yes. Data-at-rest protections are particularly important for unmanned systems that operate disconnected from networks. Full drive encryption, Pre-Boot Authentication, and storage-level protections do not depend on continuous network connectivity to protect stored data, helping maintain protection when a platform is operating remotely, offline, or has lost communications.
How do you evaluate a platform’s current data exposure?
Start by identifying what mission data the platform stores locally and what would happen if an adversary gained physical possession of the system or removed its storage. Evaluate whether authentication occurs before data becomes accessible, whether the full drive is encrypted, and what erasure and sanitization capabilities are available for loss scenarios.
Conner Crisafulli
Conner Crisafulli is a solutions engineer and cybersecurity professional at Cigent with a unique background bridging elite military operations and advanced data security. Before joining Cigent, Conner served six years as a U.S. Air Force Combat Controller, where he specialized in high-stakes mission planning, communication systems, and joint operations coordination/execution. Drawing from his experience in complex, contested environments, Conner now helps federal agencies and enterprise clients strengthen their data-at-rest protection strategies. At Cigent, he focuses on practical applications of self-encrypting drives (SEDs), pre-boot authentication (PBA), and various CSfC (commercial solutions for classified) technologies to safeguard sensitive data against evolving cyber threats.