Protecting classified data at the tactical edge is now a design requirement, not a special case. Mission data is created, processed, and retained on the platforms that carry the mission, and it stays on them after the mission ends.
Schedule a DemoMission data is no longer confined to centralized systems and secure facilities. It is created, processed, and stored on rugged endpoints, forward-deployed compute, ground control stations, vehicle systems, autonomous platforms, and other devices operating closer to the mission.
These systems support real-time intelligence, mission planning, sensor processing, command and control, AI-enabled applications, and other operational workloads. As more capability moves forward, so does the sensitive data those capabilities depend on.
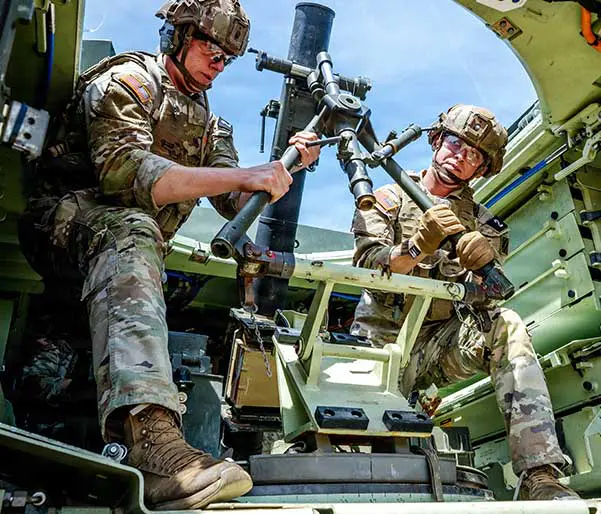
Laptops, rugged tablets, mobile workstations, and operator devices used for planning, analysis, communications, and field operations.
Deployable servers, tactical edge nodes, AI-enabled compute, and storage systems that process and retain data closer to the point of need.
Vehicle mission computers, ground control stations, unmanned platforms, autonomous systems, and supporting operator devices.
Maintenance devices, diagnostic systems, software-update platforms, and other systems used to configure and sustain fielded capability.
Mission data can remain on systems long after the operation begins, ends, or changes. That includes data created by operators, collected by sensors, cached by applications, retained in logs, or stored for transfer. That can include:
Cigent secure SSDs provide hardware full drive encryption and are paired with Cigent Pre-Boot Authentication. Protected storage remains locked until an authorized user or system successfully authenticates, extending access control to the data before the operating system loads.
Cigent Software FDE provides an independent encryption and authentication layer for additional defense in depth and can strengthen protection across systems already deployed in the field.
Deploy, manage, update, and enforce protection across distributed systems through repeatable workflows, then securely sanitize data as devices are reassigned, recovered, redeployed, or decommissioned.
Tactical programs rarely operate uniform fleets. A single deployment may include Windows and Linux systems, rugged endpoints, servers, vehicle support devices, autonomous platforms, and equipment already fielded across multiple locations.
Cigent provides flexible hardware and software protection that can be integrated into new systems or introduced across existing deployments. This gives programs a practical path to strengthen data-at-rest protection without requiring every device, platform, or refresh cycle to follow the same deployment model.
Cigent collaborated with Curtiss-Wright to bring secure storage, Pre-Boot Authentication, and DAR management capabilities to PacStar platforms used across tactical servers, edge storage systems, vehicle-mounted deployments, and forward locations.
The combined approach gives defense teams a practical path to deploy rugged mission compute with stronger protection for classified data across distributed edge environments.