Data at Rest Protection for Defense Mission Systems

Data at rest protection for classified information cannot depend on custody, connectivity, or an intact operating system. Cigent provides CSfC-listed secure storage, Pre-Boot Authentication, and Software Full Drive Encryption, the components of a layered DAR architecture, across endpoints, servers, tactical systems, and mission platforms.

Take the CSfC for DAR Assessment
Built for High-Assurance Data Protection

Classified Data Requires a Layered Architecture

Classified data increasingly resides on systems operating beyond fixed facilities, from laptops and rugged endpoints to servers, tactical compute, and unmanned platforms. When one of those systems is powered off, unauthenticated, or outside authorized control, network defenses may no longer apply. An adversary with physical possession has time, tooling, and no intention of booting the installed operating system. Data at rest protection has to hold at exactly that moment, with encryption and authentication that live on the device itself.

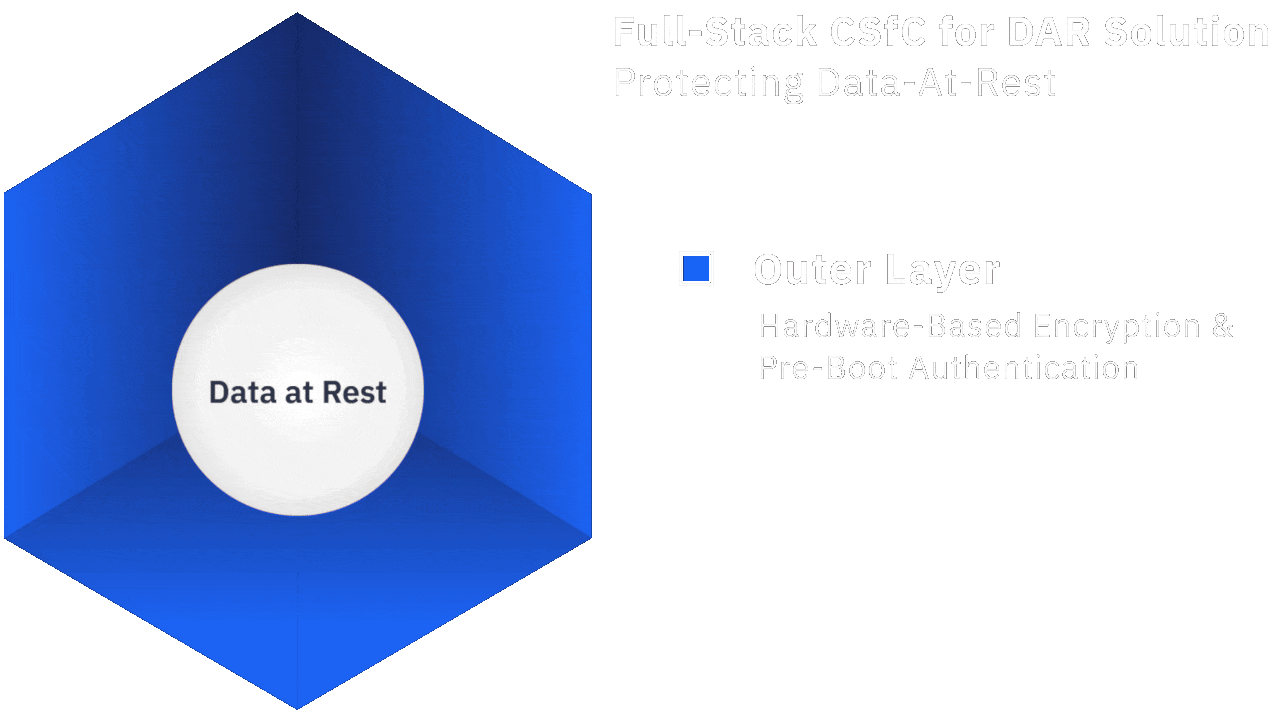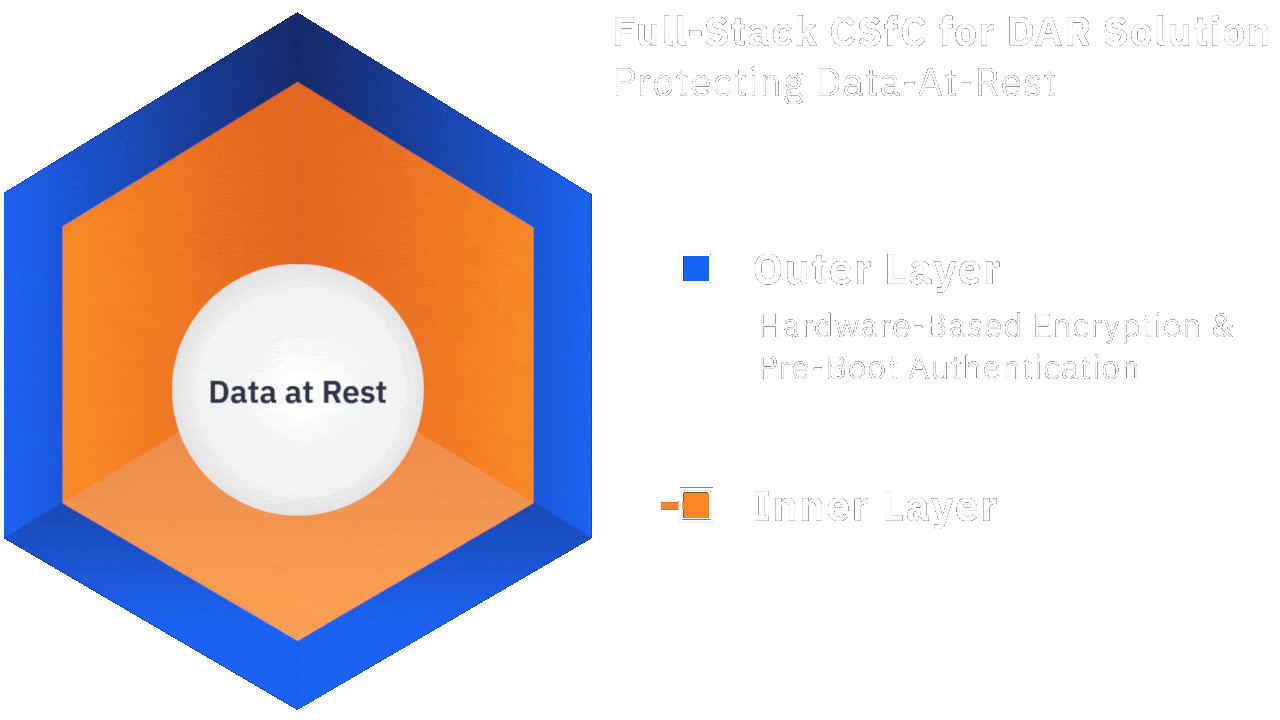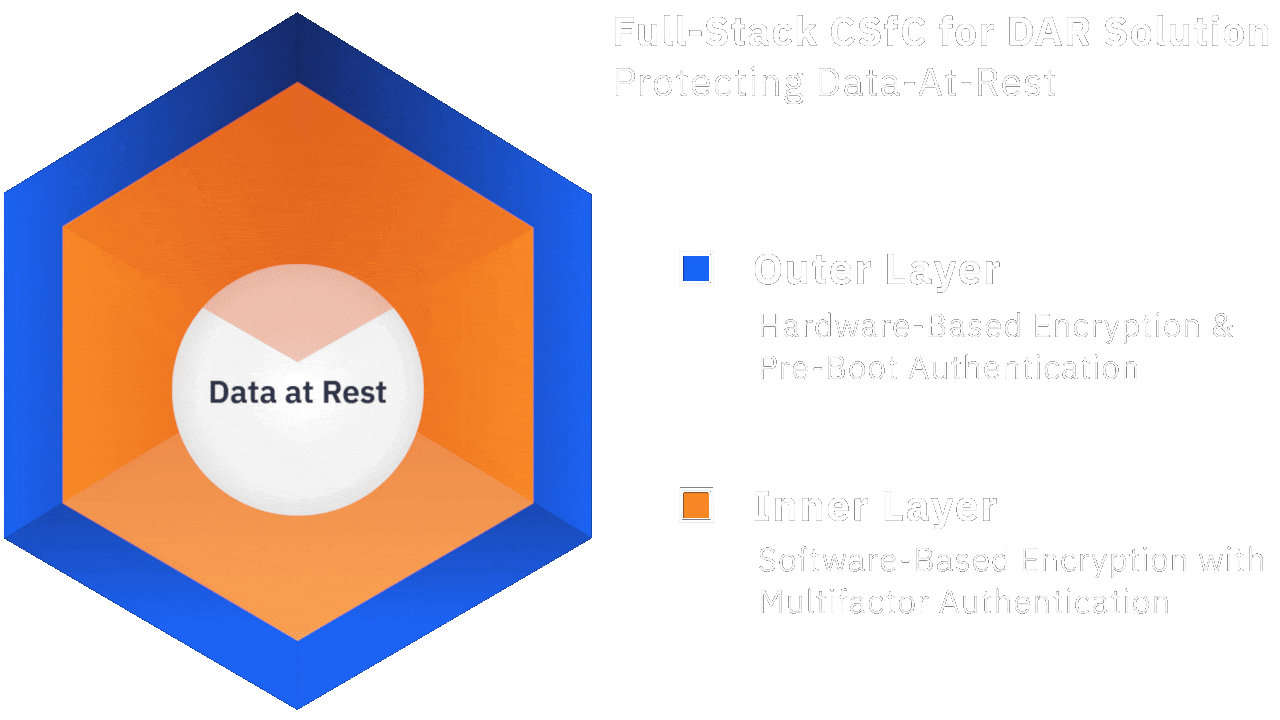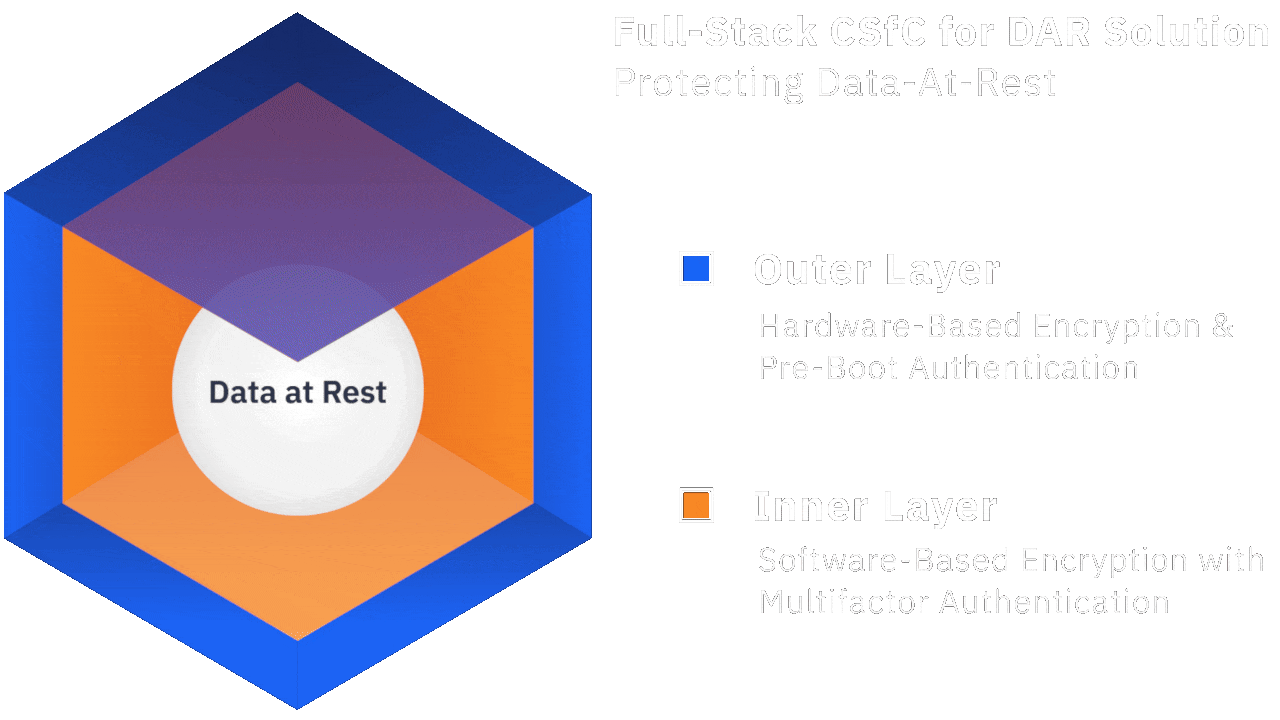
The NSA’s Commercial Solutions for Classified (CSfC) Data at Rest Capability Package, currently version 5.1.0, establishes a layered approach using two independent encryption layers to protect classified data while at rest. Cigent provides CSfC-listed secure storage, Pre-Boot Authentication, and Software Full Drive Encryption to support that architecture with encryption and authentication at each layer.
BUILT FOR THE MISSION

LAYERED DATA PROTECTION
SIMPLIFIED DEPLOYMENT
NSA CSfC LISTED
PLATFORM AGNOSTIC
HARDWARE + SOFTWARE
Meet CSfC Requirements

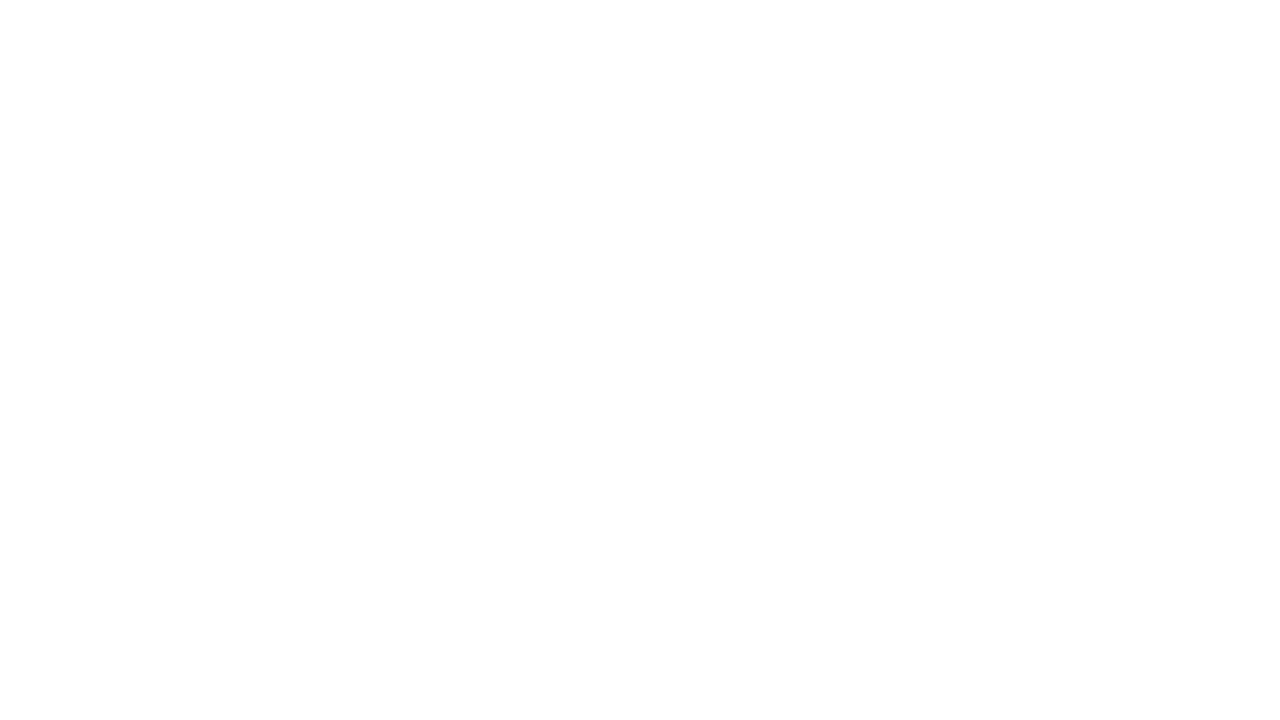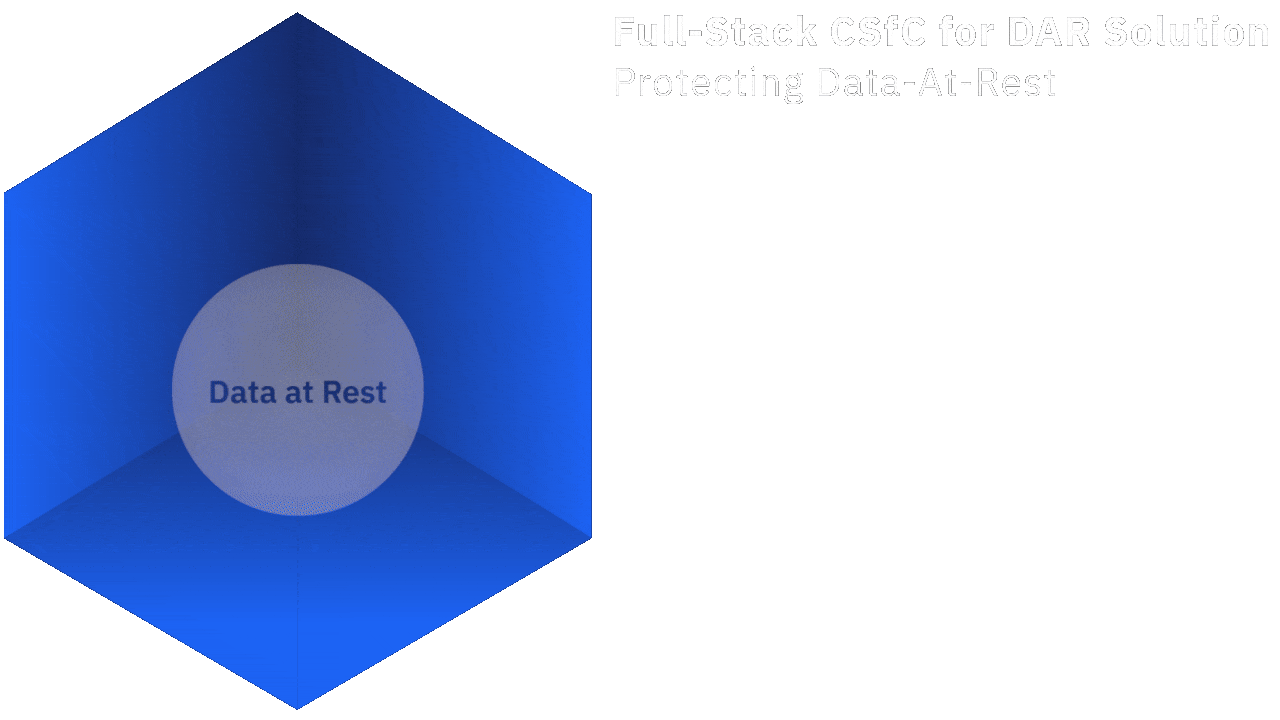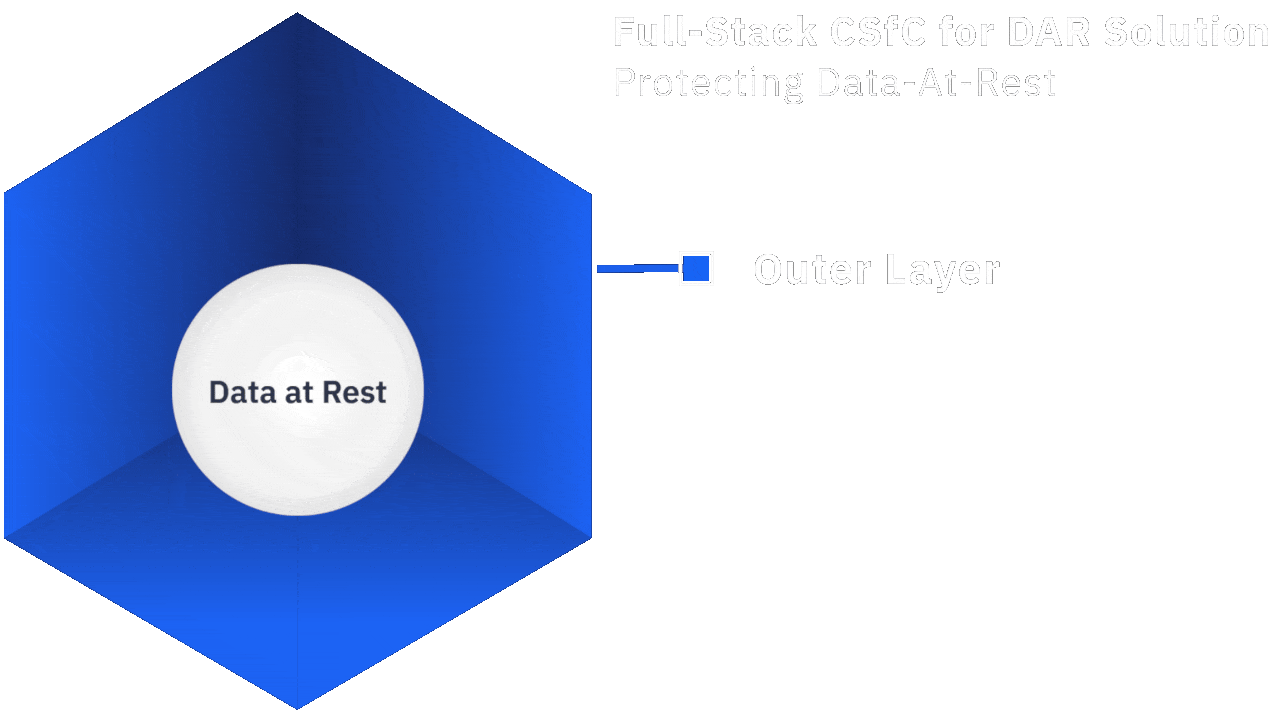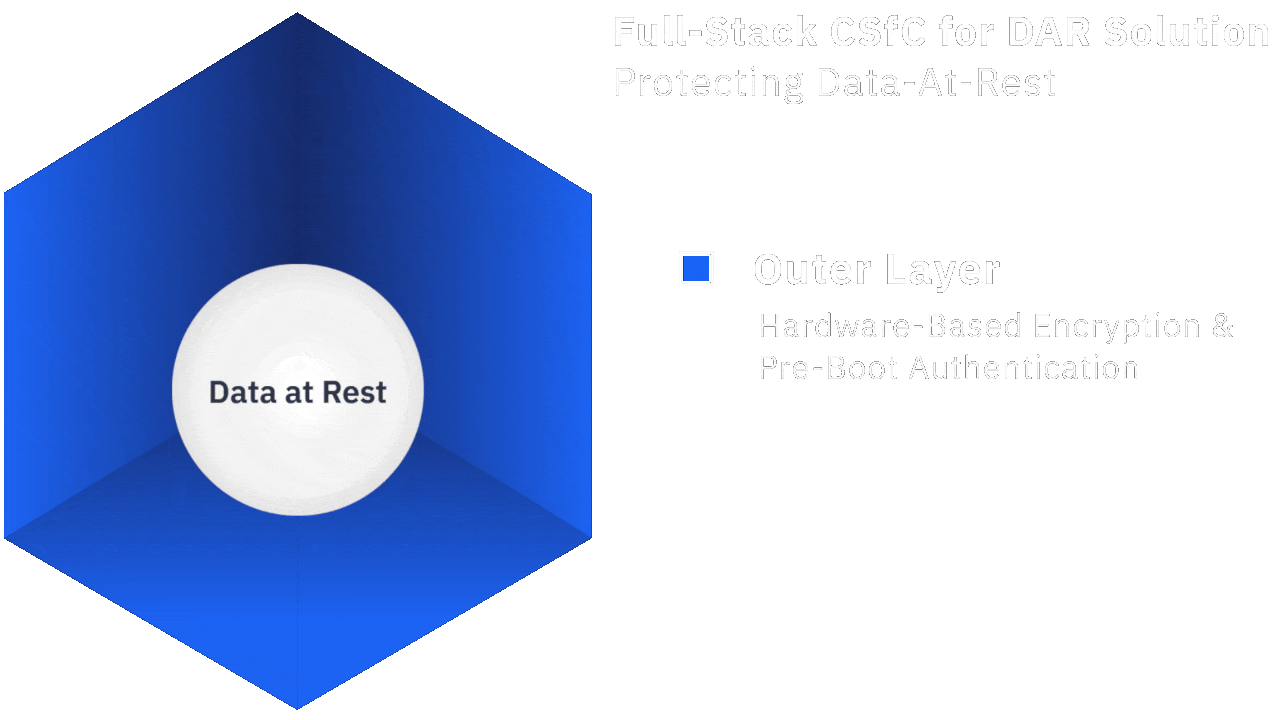
Cigent provides CSfC-listed components for both layers of the DAR Capability Package: secure storage with Pre-Boot Authentication as the outer layer and independent Software Full Drive Encryption as the inner layer.

Protect Mission Systems

Apply layered protection across client, enterprise, and embedded environments spanning endpoints, servers, tactical compute, and mission platforms.

Deploy & Manage at Scale

Configure, update, monitor, and enforce DAR protections through repeatable workflows across distributed systems and fleets.

Authenticate Before Access

Independent pre-boot and pre-OS authentication controls access before protected data becomes available to the operating environment.

Control Data Lifecycle

Maintain control from initial deployment through verified sanitization aligned with NIST SP 800-88 Rev. 2 and secure decommissioning.

Streamline Acquisition

Cigent SSDs and software are available directly from leading device manufacturers within their configuration flows, simplifying acquisition.
Cigent Protection

Understanding CSfC for DAR Protection

Includes Hardware Full Drive Encryption with PBA. This is the outer layer as it provides the initial protection layer. It includes:

  • AES-256 Hardware Full Drive Encryption
    Utilizing NSA-validated cryptography. Encryption keys are not stored in TPM or in aggregate, preventing interception or compromise.
  • Pre-boot Authentication (PBA)
    Providing a separate, secure environment to unlock drive encryption. The approach prevents an adversary from compromising the OS boot to access data.
CSfC DAR Readiness Assessment

Do CSfC Data-at-Rest Requirements Apply to Your Environment?

Not every mission environment has the same data-at-rest requirements. The Cigent CSfC DAR Readiness Assessment walks you through a short series of questions about the data you protect, the systems that store it, and how those systems are used to help determine whether CSfC DAR protections should be considered for your environment.

As classified data moves onto endpoints, tactical systems, servers, and mission platforms outside traditional secure facilities, understanding the required level of protection becomes increasingly important. Use the assessment to identify potential CSfC DAR requirements and better understand when a layered encryption and authentication architecture may be appropriate.

eBook

Protect Your Data at Rest

Cigent is prepared to support your mission, navigating the complex compliance requirements to protect data at the edge. Its solutions were developed for and with US Federal agencies with deep expertise in data protection. Read our extensive eBook to learn more.

The Cigent Advantage

Cigent components are listed on the NSA CSfC Components List for protecting classified data at rest. Security functionality is evaluated through NIAP Common Criteria and cryptography is validated under NIST programs. Cigent solutions were designed and developed with and for US Intelligence and Defense communities. All employees, including Cigent software development, are based in the US. The team includes multiple personnel with TS/SCI clearance with decades of data protection and operational experience to support your requirements.

Cigent solutions have been tested and validated by leading Federal agencies including MITRE, NIST, NSA, NIAP, the Air Force, Cyber Resilience of Weapon Systems (CROWS), and NSSIF (UK) and are deployed across US Intelligence agencies, US Defense services, and the defense industrial base.

The Latest from Cigent

View All

Frequently Asked Questions

Still have Questions?

Learn how to secure mission-critical and classified data across the battlespace.

Download eBook

See Where Your Architecture Stands

Answer a short series of questions about your data, your systems, and how they deploy. The assessment shows whether CSfC DAR requirements apply to your environment and where your architecture already meets them.

Take the CSfC for DAR Assessment